PHP has been fairly safe for the most part. We didn’t have a lot of those in the last 10 years.
The most notable one was in 2019 where PHP-FPM was vulnerable under nginx. Other than that, I can’t remember anything and I’m working with PHP for over a decade. There were some bugs that look very severe, but require access to the system first, making them relatively harmless.
I had much more emergency patchdays because of nodejs and that entire garbage ecosystem.
You’re painting PHP as a language that is so riffled with vulnerabilities that more than 4 are found every week which isnot just dishonest, its just plain bullshit.
Its really weird to me to see people shit on PHP while never having used it or read anything about it; people just say it sucks because thats what they’ve read from some other idiot making the same vapid claims
Back when it was new, and we used Perl CGI for everything, it was genuinely a security improvement, even though it had its own issues (often). The main trouble was that people didn’t know how to sandbox it. I ran PHP-CGI for a number of years standard before php-fpm made sandboxing easier.

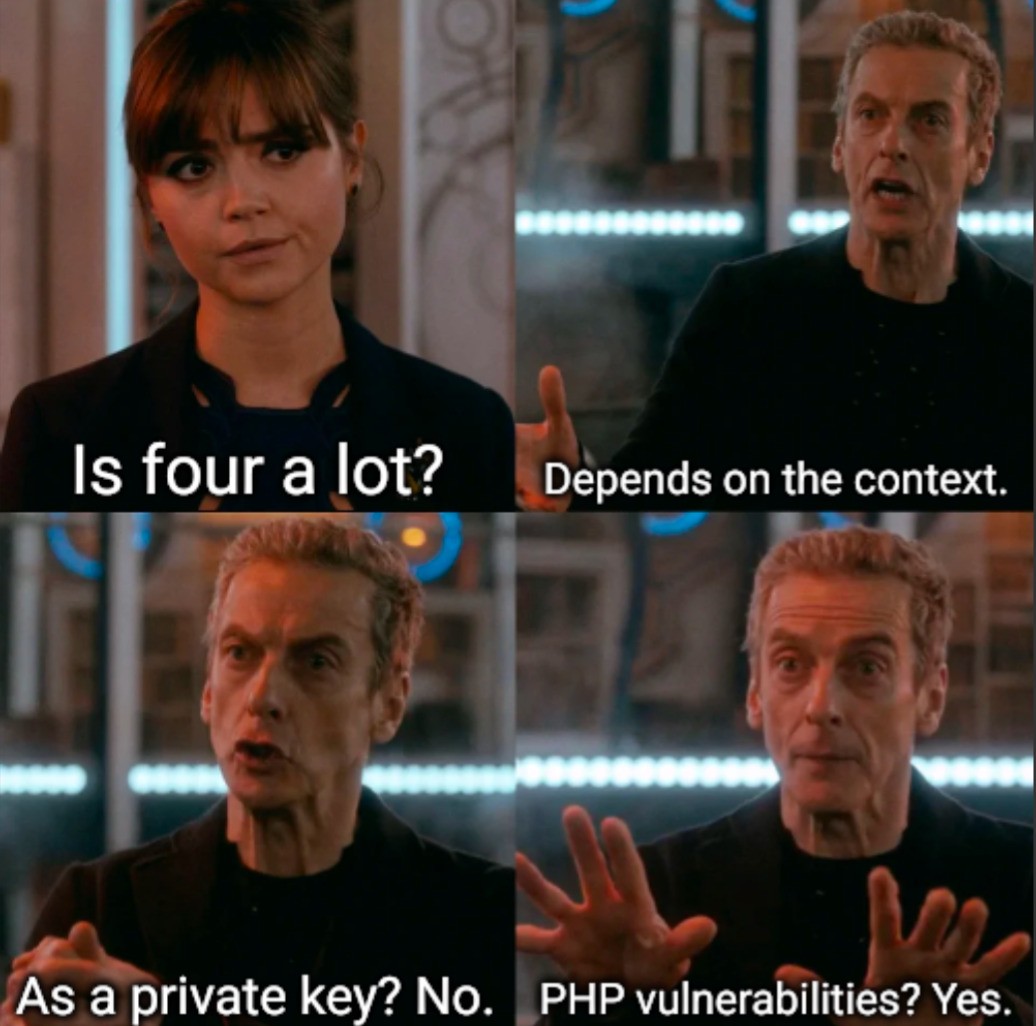
Let’s be honest: four isn’t a lot in terms of PHP vulnerabilities, either. At least not unless you qualify it with “per week.”
PHP has been fairly safe for the most part. We didn’t have a lot of those in the last 10 years.
The most notable one was in 2019 where PHP-FPM was vulnerable under nginx. Other than that, I can’t remember anything and I’m working with PHP for over a decade. There were some bugs that look very severe, but require access to the system first, making them relatively harmless.
I had much more emergency patchdays because of nodejs and that entire garbage ecosystem.
Let’s be honest : you’re dishonest
You’re painting PHP as a language that is so riffled with vulnerabilities that more than 4 are found every week which isnot just dishonest, its just plain bullshit.
Its really weird to me to see people shit on PHP while never having used it or read anything about it; people just say it sucks because thats what they’ve read from some other idiot making the same vapid claims
Back when it was new, and we used Perl CGI for everything, it was genuinely a security improvement, even though it had its own issues (often). The main trouble was that people didn’t know how to sandbox it. I ran PHP-CGI for a number of years standard before php-fpm made sandboxing easier.